FINANCIAL SERVICES
A control that passed is not the same as an exposure you can explain
Separation of duties is enforced system by system. Authority is not. The Gathid Authority Map models how privilege combines across payments, trading, ledger, and supporting platforms, and exposes the pathways those combinations create.
Where authority accumulates in financial services
Access in a bank, insurer, or asset manager is granted one platform at a time. One application lets an identity create a counterparty. Another lets an identity approve a transaction. A third releases the payment. Reviewed individually, each grant looks reasonable and each control passes. Combined, they form a pathway, and no single system was built to show it.
-
Separation of duties enforced inside applications, but not across them
-
Long-standing exception approvals that were never structurally unwound
-
Outsourced operations, offshore teams, and vendor administrators holding standing access
-
Service accounts moving value between core systems with unclear ownership
Why current governance does not answer the question
CPS 234, CPS 230, SOX, and DORA obligations are met by demonstrating that controls are designed, operating, and tested. That evidence answers whether process was followed. It does not answer what a single misused identity could set in motion across the estate today, and regulators increasingly ask the second question rather than the first.
What the Gathid Authority Map shows
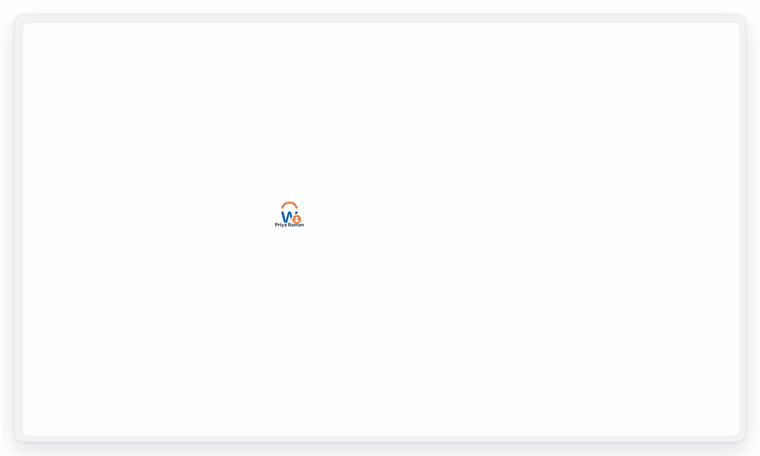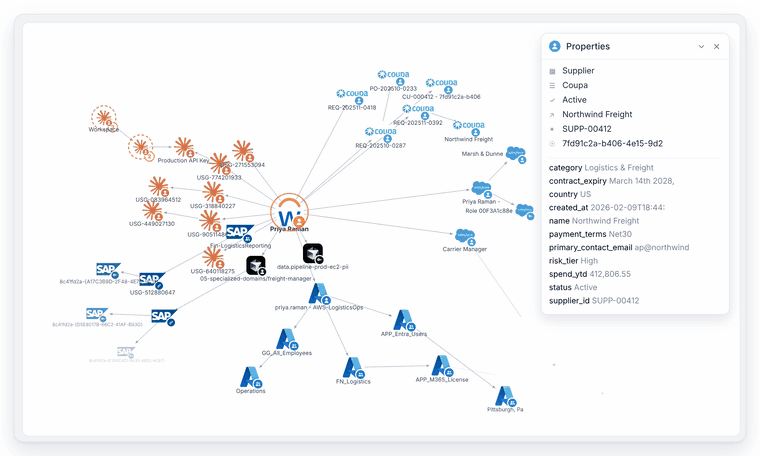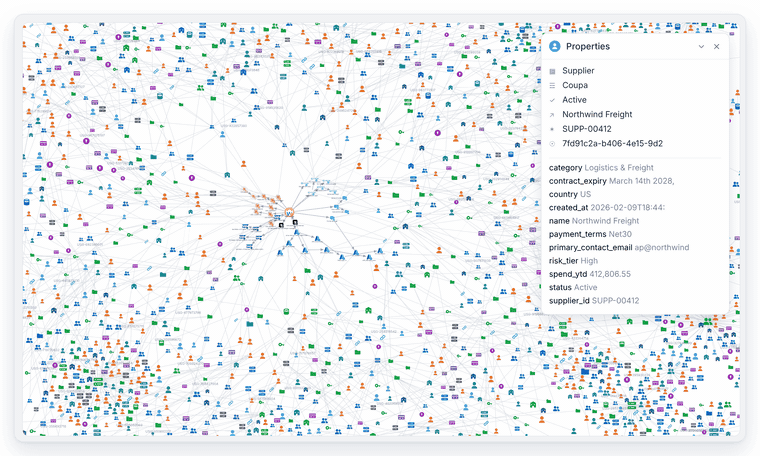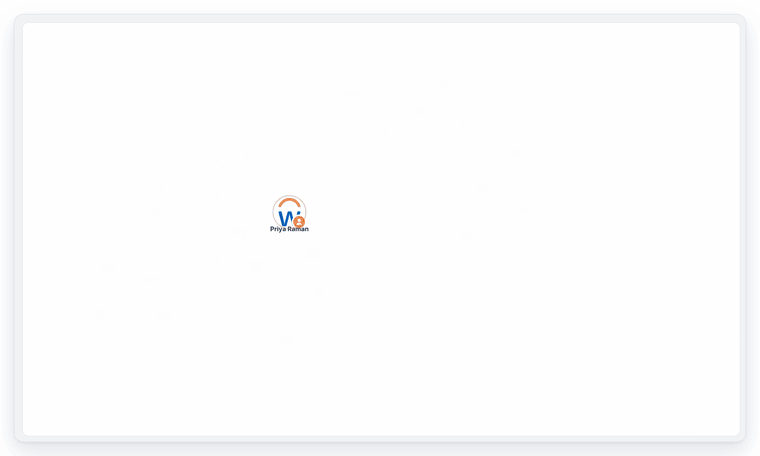
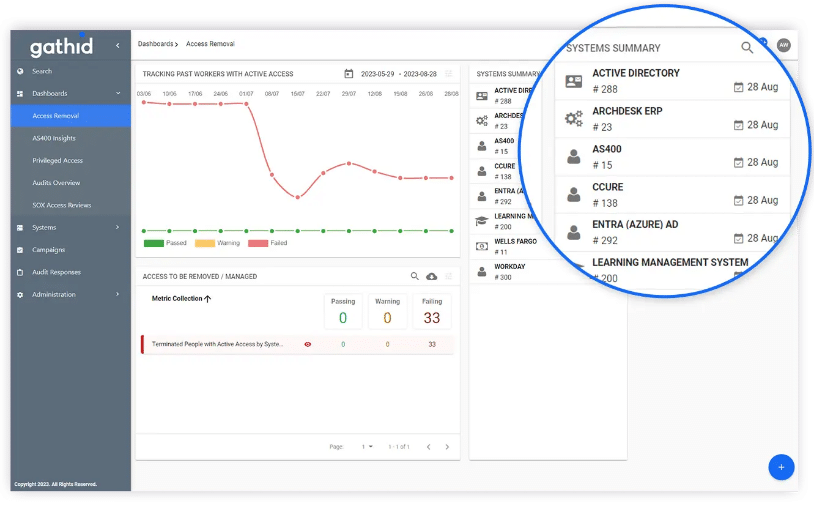
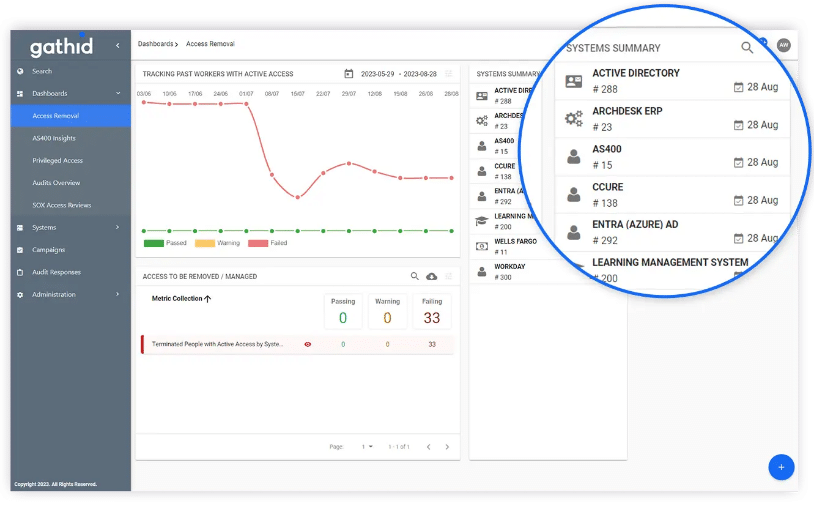
Gathid maintains a current, queryable model of authority across the systems in scope, built from complete data sets rather than sampled extracts.
-
Toxic combinations that only exist once authority is resolved across systems
-
Authority pathways from origination through approval to settlement
-
Effective authority held by outsourced, delegated, and vendor identities
-
Authority concentration in operations, treasury, and platform administration
-
Authority drift between reporting periods, made visible rather than assumed
What this makes possible
-
Structural separation of duties assurance that is defensible in front of a regulator, not only an auditor
-
Blast radius stated for a named identity, account, or credential, rather than estimated
-
Third-party and outsourcing risk assessed on effective authority rather than contractual scope
-
A prioritized remediation sequence that reflects consequence, not finding volume
How Gathid fits your stack
Alongside your stack, not instead of it. Gathid works with the IAM, IGA and PAM platforms the agency has already invested in, giving them a complete picture of authority to act on.
Understand, measure, control. Authority structures you can see, quantify and change deliberately, rather than discover during an incident or an audit.
Connected to where the work happens. The Gathid Authority Map is reachable through the API and a permission-scoped MCP server, and raises notifications and tickets in the service management systems your agency already runs.
Attributable by design. The model reasons, your people decide. Every change stays traceable to the officer who approved it, which is what makes the evidence hold in front of an audit office.
Book a Business Authority Exposure Briefing
Before Gathid, managing identity access felt like a maze. Now, it's streamlined and secure. A game-changer for our cybersecurity."
The Power of Gathered Intelligence
Inspired by the power of gathered identities, Gathid pinpoints identity and access anomalies, symbolized by our iconic blue dot. This isn’t just pattern recognition; it’s 20 years of expertise in distinguishing critical insights from the noise to ensure the integrity and security of your identity information across your systems.
Why Choose Us

Expertise & Experience
Gathid stands out with over two decades of industry leadership, offering unrivaled insights and proven solutions across complex identity landscapes.

Proactive Approach
Gathid helps anticipate and mitigate identity threats before they arise, ensuring your digital ecosystem remains resilient against emerging challenges.

Scalable
Solution
Our scalable solution adapts to your growing needs, ensuring seamless integration and performance regardless of your organization’s size.

End-to-End
Support
From initial consultation to ongoing utilization, Gathid provides comprehensive support, ensuring your identity governance framework thrives.
We partner with forward-thinking companies in sectors like mining, manufacturing and banking (spanning 1,000 to 100,000 employees) who put a premium on cutting-edge technology and ironclad security.
Frequently Asked Questions
What is Enterprise Authority Assurance?
It is knowing, at any moment, what every identity in the firm could set in motion across its systems, and being able to prove it. Control testing records whether a control was designed, operated and tested. Authority assurance models what the grants behind those controls add up to once inheritance, delegation and system relationships are resolved, so the firm can answer a structural question with evidence rather than a test result.
What is a toxic combination, and why doesn’t our SoD tooling catch it?
A toxic combination is a set of entitlements that are individually acceptable and jointly dangerous: create a counterparty in one system, approve a transaction in another, release the payment in a third. Separation of duties tooling is strong inside each application, because each application knows its own roles. The combination only becomes visible once authority is resolved across all three, and no single system holds that view. Gathid builds it.
What does “blast radius” mean here?
Blast radius is the full set of actions a named identity, account or credential could take across the estate if it were misused, after every pathway is followed to its end. Most firms estimate it from role descriptions. Gathid states it from the model, which is the difference between an assumption and an answer a regulator will accept.
How is this different from an access review or control testing?
An access review establishes that a reviewer examined a list of entitlements and signed. Control testing under CPS 234, CPS 230, SOX or DORA establishes that a control exists and operated as designed. Both describe process. Neither states what a specific identity could reach across payments, trading and ledger platforms right now. Gathid answers that structural question, and the existing frameworks continue to answer the control question.
How does Gathid support CPS 234, CPS 230, SOX and DORA obligations?
Gathid is not a certification and does not replace testing. It adds the evidence those regimes increasingly ask for: a current, traceable statement of effective authority for any identity, drawn from complete data rather than sampled extracts. For CPS 230 and DORA that includes the effective authority held by material service providers and vendor administrators. For SOX it includes structural separation of duties across the systems that feed financial reporting, rather than within each one.
Can we use Gathid to answer a regulator’s question about a specific identity?
Yes. When a regulator asks what a named account or credential could do, the firm can produce the pathways it holds, the systems those reach, the owner accountable for each, and the approvals that created them. Because the model is rebuilt from source data and every change is attributable, the answer holds up under follow-up questions, which is where estimates usually fail.
The Power of Gathered Intelligence