COMPLIANCE AND RISK
A completed review is evidence of process. It is not evidence of exposure
Your risk register carries identity risk as a rating. The Gathid Authority Map lets you support that rating with structure: what authority exists, where it concentrates, and what it would make possible.
The evidence problem
Identity risk is one of the few enterprise risks still assessed largely on attestation. Controls are documented, tested, and signed off, and the resulting evidence describes the control rather than the exposure. When a regulator, an internal audit function, or a board risk committee asks what the residual exposure actually is, the honest answer is usually an informed estimate.
-
Control completion recorded where control effectiveness was intended
-
Point-in-time sampling used to describe a continuously changing structure
-
Separation of duties assured inside applications but not across them
-
Third-party exposure assessed on contracted scope rather than effective authority
What structural evidence looks like
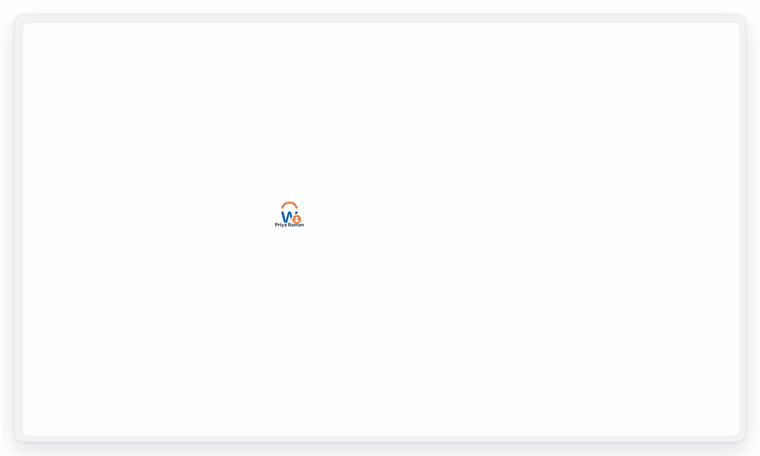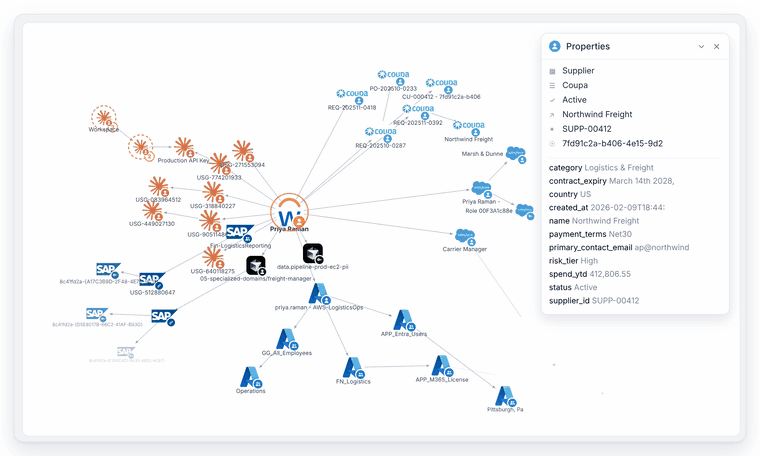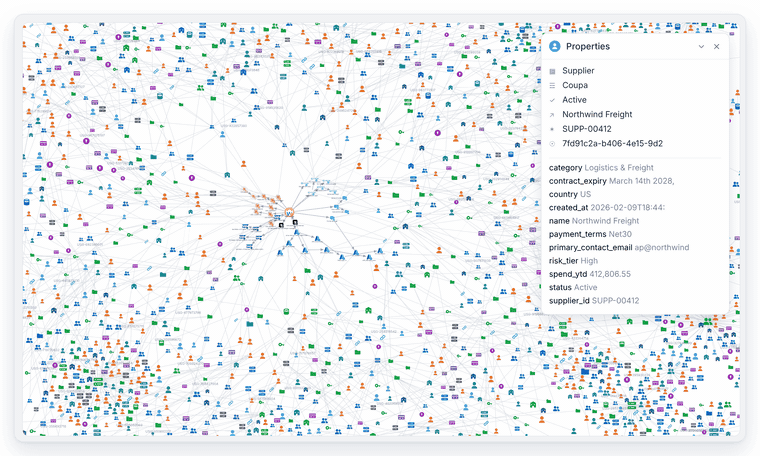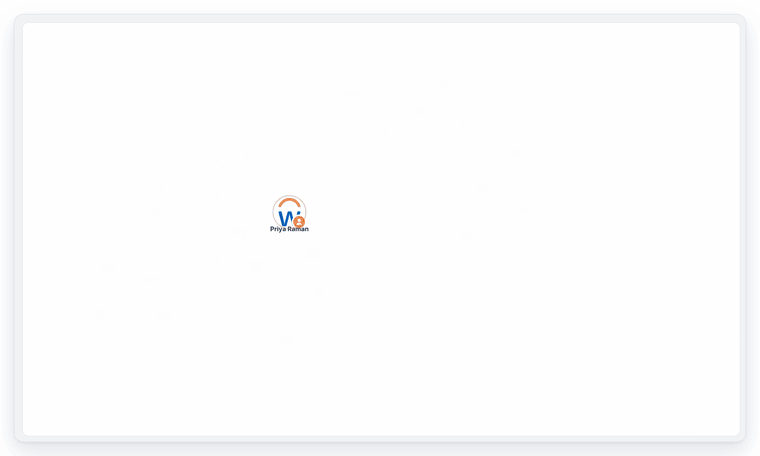
Gathid models the relationships between identities, accounts, systems, roles, and credentials across the systems in scope, then makes that model queryable. The output is not a finding list. It is a structure you can interrogate, reproduce, and defend.
-
Effective authority for any identity, after inheritance and delegation are resolved
-
Toxic combinations that exist only once authority is resolved across systems
-
Authority concentration, quantified rather than described
-
Authority drift between rebuilds, which is the measurable form of control decay
-
Ownership gaps, where authority exists without an accountable owner
What changes in practice
-
Identity risk ratings supported by structural evidence rather than attestation alone
-
Regulatory responses that describe exposure, not only control design
-
Audit findings prioritized by consequence, with a defensible basis for the ordering
-
Reproducible answers, because a query against the model returns the same result for anyone who runs it
How Gathid fits your stack
Alongside your stack, not instead of it. Gathid works with the IAM, IGA and PAM platforms the agency has already invested in, giving them a complete picture of authority to act on.
Understand, measure, control. Authority structures you can see, quantify and change deliberately, rather than discover during an incident or an audit.
Connected to where the work happens. The Gathid Authority Map is reachable through the API and a permission-scoped MCP server, and raises notifications and tickets in the service management systems your agency already runs.
Attributable by design. The model reasons, your people decide. Every change stays traceable to the officer who approved it, which is what makes the evidence hold in front of an audit office.
Book a Business Authority Exposure Briefing
Before Gathid, managing identity access felt like a maze. Now, it's streamlined and secure. A game-changer for our cybersecurity."
The Power of Gathered Intelligence
Inspired by the power of gathered identities, Gathid pinpoints identity and access anomalies, symbolized by our iconic blue dot. This isn’t just pattern recognition; it’s 20 years of expertise in distinguishing critical insights from the noise to ensure the integrity and security of your identity information across your systems.
Why Choose Us

Expertise & Experience
Gathid stands out with over two decades of industry leadership, offering unrivaled insights and proven solutions across complex identity landscapes.

Proactive Approach
Gathid helps anticipate and mitigate identity threats before they arise, ensuring your digital ecosystem remains resilient against emerging challenges.

Scalable
Solution
Our scalable solution adapts to your growing needs, ensuring seamless integration and performance regardless of your organization’s size.

End-to-End
Support
From initial consultation to ongoing utilization, Gathid provides comprehensive support, ensuring your identity governance framework thrives.
We partner with forward-thinking companies in sectors like mining, manufacturing and banking (spanning 1,000 to 100,000 employees) who put a premium on cutting-edge technology and ironclad security.
Frequently Asked Questions
What is Enterprise Authority Assurance, from a risk and compliance point of view?
It is a way to support an identity risk rating with structure rather than attestation. Control testing produces evidence that a control was designed, operated and signed off. Authority assurance produces evidence of what the authority behind those controls actually makes possible: what any identity could reach once inheritance, delegation and cross-system relationships are resolved, where that authority concentrates and where it has no owner. The first describes the control. The second describes the exposure.
What is the difference between control completion and control effectiveness here?
Completion means the review ran and the attestation closed. Effectiveness means the control reduced exposure, and that can only be shown by looking at the structure the control was meant to govern. A review that certifies ten thousand entitlements one at a time can complete perfectly while leaving a cross-system combination untouched, because the combination was never in any reviewer’s list. The map measures the structure, so effectiveness can be shown rather than inferred from completion.
What does “structural evidence” mean, and how is it different from a finding list?
A finding list is a set of exceptions somebody noticed, in the order they were noticed. Structural evidence is a model you can interrogate: ask what a named identity could reach, which identities could originate, approve and settle, how much authority sits in the top twenty accounts, and get an answer drawn from complete source data. The same query returns the same answer for anyone who runs it, which is what makes it reproducible and defensible.
Will a regulator or external auditor accept Gathid as evidence?
The evidence has the properties regulators ask for: it is drawn from complete data rather than samples, it is reproducible by anyone with the same access, and every change to the structure is attributable to the person who approved it.
How does Gathid change what we put in the risk register?
Identity risk usually appears as a rating supported by control status. The map lets the rating be supported by measures that move: the number of identities with critical reach, the degree of authority concentration, the count of toxic combinations open across systems and the volume of authority with no accountable owner. Those can be tracked between reporting periods, which turns a qualitative rating into one with a quantitative basis.
Can we use Gathid to answer a regulatory request about a specific identity or process?
Yes. When a supervisor asks what a named account could do, or whether any identity can originate, approve and settle within a process, the response can describe exposure from the model rather than control design from the policy. The pathways, the owners and the approvals that created them are part of the answer, which is what holds under follow-up questions.
The Power of Gathered Intelligence